
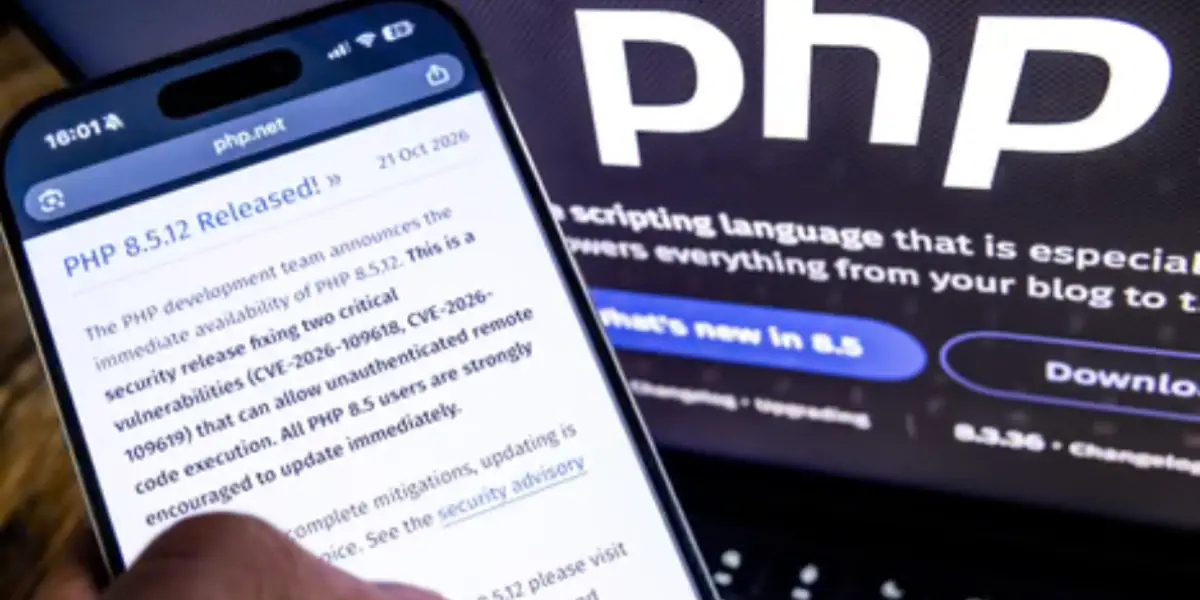
Kathmandu. A cyber security expert has warned that around 30 million websites around the world may be affected due to serious security flaws found in PHP, a programming language widely used in website creation. Millions of government sites around the world, including Nepal, are closed.
According to Alan Woodward, a British cyber security expert and professor at the University of Surrey’s Center for Cyber Security, by exploiting these vulnerabilities, attackers can place their own code on the website’s server and perform unauthorized activities on it.
Speaking on BBC Radio Four’s ‘Today’ programme, he said there was a risk of stealing personal data, accessing other parts of the organisation’s network or putting a ‘backdoor’ into the server to regain access in the future.
According to Woodward, companies that monitor online activity, such as Amazon and Cloudflare, have seen signs that vulnerable websites are being tested. But he clarified that there is no confirmation whether the websites have been attacked or not.
AI increases the risk of exploiting vulnerabilities
According to Woodward, these flaws in AJA were discovered by humans in 2024. But at that time it was considered too complicated to abuse them.
He said that with the development of artificial intelligence technology including large language models (LLM), a practical way to exploit these weaknesses has been discovered.
He says that in the last one week, behind the scenes, work is being done on the possibility of exploiting such weaknesses.
He also said that the details of the necessary update or ‘patch’ to solve the security flaw may have been released before it was made public. This may have given an attacker the opportunity to identify a vulnerable system before a security update was available.
Vigilance in various countries, including the UK
The UK government says it is working to identify the potential impact of these vulnerabilities on its online services. The government spokesperson has asked all organizations in the private and public sectors, large and small, to follow the instructions issued to keep their systems safe.
The UK’s National Cyber Security Center (NCSC) along with the equivalent bodies of the European Union and Australia have urged organizations using AJA to implement security updates immediately.
If it is not possible to implement security measures immediately, the NCSC suggests that the system should be kept offline until it is fully secured.
According to previously published details, the developer has released a security update to fix AJA’s vulnerability. Apart from applying updates to affected systems, cyber security agencies have also asked to check the possibility of ‘backdoors’ that can be used by attackers to maintain unauthorized access.
Experts warn that even though the estimate that around 30 million websites may be affected shows the potential extent of this problem, it does not mean that all websites have been affected. The actual risk will depend on the AJA version the website is using, whether or not security updates have been applied, and whether vulnerabilities in the system have been exploited.